Devon Bennett · 11 September 2026
Navigating Data Protection Challenges Among Independent Site Operators in Competitive Niches
Independent site operators in competitive niches face mounting pressure to manage personal data while maintaining operational efficiency, and regulatory frameworks continue to evolve across regions. Data protection requirements now span multiple jurisdictions, with rules that affect everything from user consent mechanisms to third-party data sharing arrangements. Operators in sectors such as affiliate marketing, specialized content platforms, and niche e-commerce must track these developments closely because violations carry financial penalties and reputational damage that smaller teams struggle to absorb.
Regulatory Frameworks Shaping Current Practices
Legislation such as the European Union's General Data Protection Regulation and California's Consumer Privacy Act set baseline standards that many independent operators reference when building compliance programs. These rules require clear disclosure of data collection purposes, mechanisms for users to request deletion, and documentation of processing activities. In September 2026 several jurisdictions plan to introduce updated enforcement guidelines that tighten definitions around automated decision-making, forcing operators to audit algorithms that personalize content or recommendations.
Canadian and Australian privacy statutes add further layers, each with distinct notification timelines and consent standards. Operators who serve audiences across borders therefore maintain separate policy documents and technical controls rather than relying on a single global template. Research from academic institutions indicates that sites operating in multiple regulatory zones allocate between 15 and 25 percent of annual development budgets to compliance tooling, a figure that rises sharply when new rules take effect.
Technical and Operational Hurdles
Independent teams often rely on shared hosting environments and off-the-shelf analytics platforms, yet these tools frequently transmit user data to third parties without granular controls. Cookie consent banners must now distinguish between essential functions and marketing trackers, and many operators discover that default settings from popular plugins fail to meet updated consent standards. Log files that once seemed innocuous now fall under scrutiny when they contain IP addresses or device fingerprints that qualify as personal information.
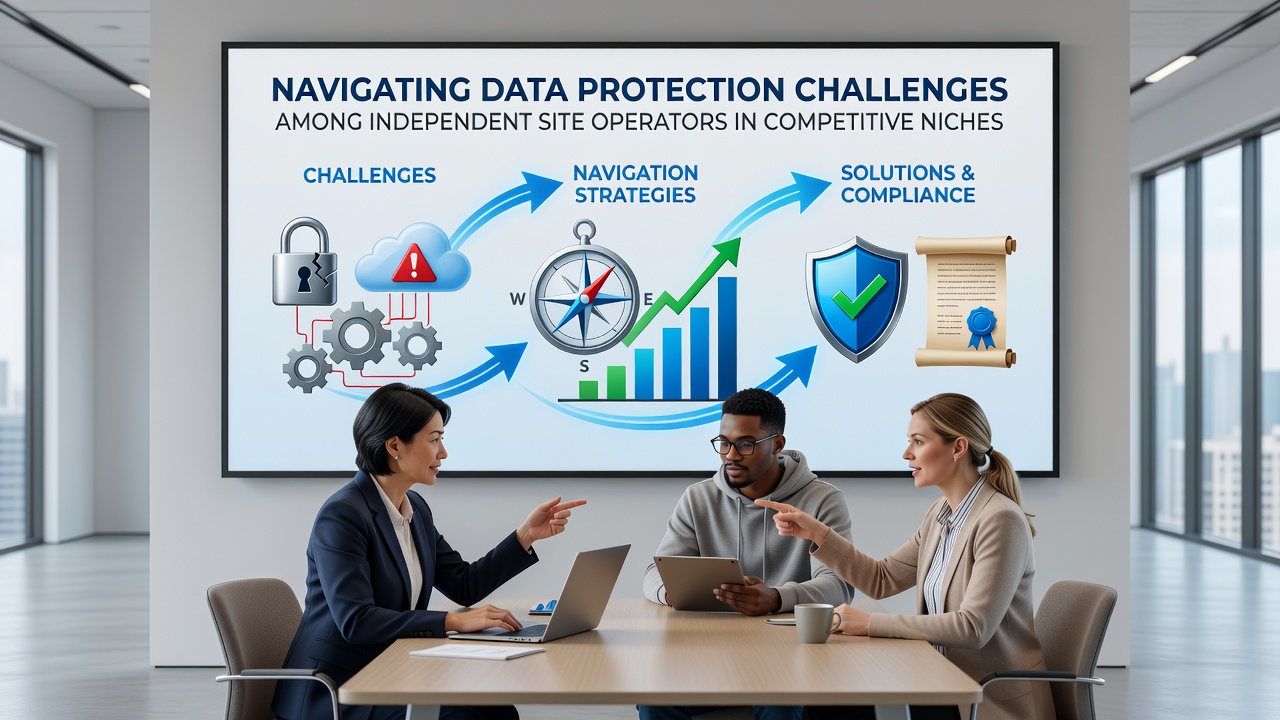
Competitive niches intensify these issues because traffic sources demand rapid iteration on landing pages and tracking pixels. One operator who manages several review sites reported that adjusting consent flows after each regulatory update required halting new feature releases for weeks at a time. Data retention schedules also create tension: competitive analysis tools benefit from historical user behavior patterns, yet deletion requests must be honored within strict windows that leave little room for aggregated reporting.
Practical Approaches Adopted by Site Operators
Many independent operators now implement data minimization principles at the architecture level, collecting only fields required for core functionality and discarding ancillary identifiers after short periods. Server-side processing replaces some client-side scripts, reducing the volume of data exposed to browser-based trackers. Documentation practices have shifted as well, with operators maintaining detailed records of data flows that regulators can review during audits.
Industry reports from organizations such as the Information Commissioner's Office highlight that sites using privacy-by-design frameworks encounter fewer enforcement actions. Operators also turn to open-source consent management solutions that allow code-level customization without recurring licensing fees. Training programs for freelancers and contractors have become standard, ensuring that anyone touching user data understands retention limits and access controls.
Emerging Trends Through Late 2026
Automated compliance scanners integrated into content management systems are gaining traction, flagging potential violations before pages publish. Cross-border data transfer agreements continue to require updates following court decisions that invalidate previous adequacy frameworks. Operators who maintain relationships with legal counsel in multiple regions report faster adaptation when guidance changes, although smaller teams often pool resources through industry associations to share interpretation costs.
Figures from research institutions show that sites in high-competition niches experience a 30 percent higher rate of data subject access requests compared with generalist publications, largely because engaged audiences actively exercise rights to access or deletion. This pattern forces operators to build self-service portals rather than handling each request manually.
Conclusion
Independent site operators continue to refine data protection strategies as regulations tighten and user expectations rise. Those who integrate compliance into daily workflows rather than treating it as periodic maintenance encounter fewer disruptions when new rules activate. Ongoing monitoring of enforcement trends across jurisdictions remains essential for teams that operate without dedicated legal departments, and technical choices made today directly influence the cost of future adaptations.